n8n (OIDC)
n8n workflow automation with single sign-on through any OIDC provider.
- n8nio/n8n:2.30.1
- port 6111
- Productivity
Web App
/http://localhost:6111/ n8n with a bolt-on OIDC login, so you can sign in through Pocket ID, Authentik, Keycloak or any other OIDC provider. It uses the community n8n-oidc hook. It is not an official n8n feature.
Features
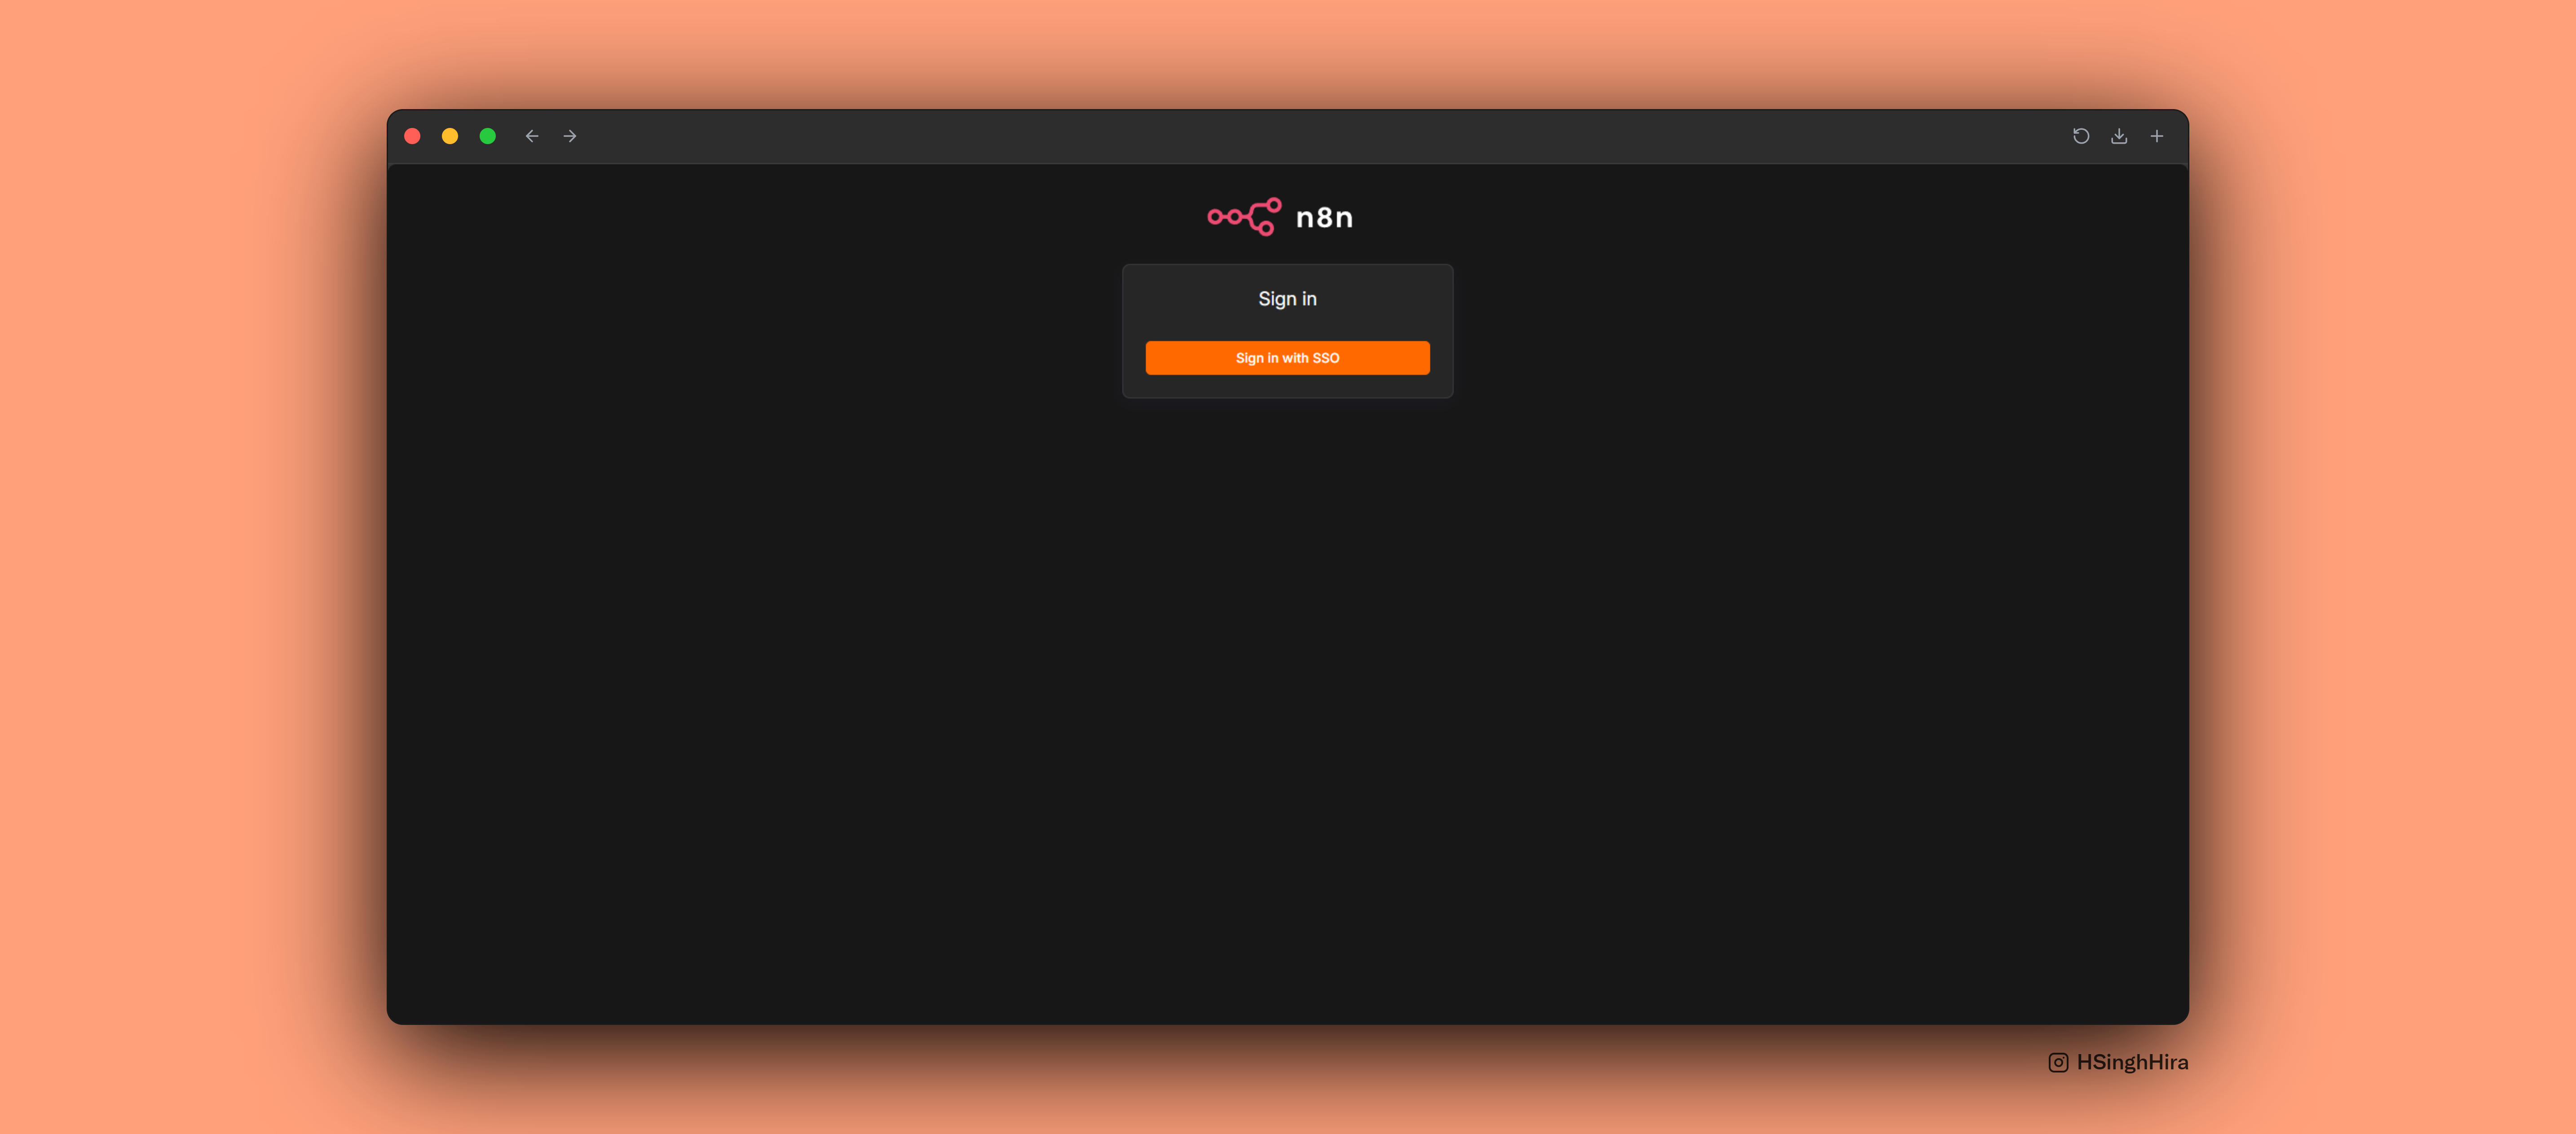
- "Sign in with SSO" button on the n8n sign-in page
- Accounts are created on first login
- The first person to sign in becomes the owner
- SQLite database and settings kept in the app data folder
- The hook file is downloaded and checked against a fixed SHA-256 hash on every start
How to use
- Open n8n from your dashboard.
- Click Sign in with SSO and log in with your provider.
- Build your first workflow.
Before you install
In your login provider, make a new OIDC client for n8n with the redirect URI http://your-server-ip:6111/auth/oidc/callback. Then fill in OIDC_ISSUER_URL, OIDC_CLIENT_ID, OIDC_CLIENT_SECRET and OIDC_REDIRECT_URI in place of the CHANGEME values. Everyone who can sign in through that client gets an n8n account, and the first one becomes the owner, so only let people you trust use it. If you use an HTTPS address, set N8N_SECURE_COOKIE to true and add N8N_PROTOCOL=https from the Variables tab.
The settings in the first table are already in the app settings. To use any other one, open the app settings, add the variable with your value, save, and the app restarts with it. A setting you leave out uses its default.
In the app settings
| Variable | Default value | Description |
|---|---|---|
TZ | $TZ | Your time zone. ZimaOS fills this in for you. |
N8N_ | false | Keep false when you open n8n with http://. Set it to true only when n8n is behind HTTPS. |
EXTERNAL_ | /home/node/.n8n/hooks.js | Path to the OIDC hook file. Do not change. |
EXTERNAL_ | /assets/oidc-frontend-hook.js | Loads the SSO button on the sign-in page. Do not change. |
N8N_ | auth | Lets the /auth/oidc routes work. Do not change. |
OIDC_ | CHANGEME_OIDC_ISSUER_URL | The address of your login provider, like https://auth.example.com. It must serve /.well-known/openid-configuration. |
OIDC_ | CHANGEME_OIDC_CLIENT_ID | The Client ID your login provider gave you for n8n. |
OIDC_ | change-me | The Client Secret your login provider gave you for n8n. |
OIDC_ | CHANGEME_OIDC_REDIRECT_URI | Your n8n address plus /auth/oidc/callback, like http://192.168.1.10:6111/auth/oidc/callback. It must match the redirect URI set in your login provider. |
Server
| Variable | Default value | Description |
|---|---|---|
N8N_ | http | Set to https when you open n8n through an HTTPS address. Also set N8N_SECURE_COOKIE to true. |
N8N_ | localhost | The host name people use to reach n8n, like n8n.example.com. |
WEBHOOK_ | — | The public address for webhooks, like https://n8n.example.com/. Set it when n8n is behind a reverse proxy so webhook links are right. |
Sign in with OIDC
| Variable | Default value | Description |
|---|---|---|
OIDC_ | openid email profile | The scopes n8n asks your login provider for, separated by spaces. |
Logs
| Variable | Default value | Description |
|---|---|---|
N8N_ | info | How much detail goes in the log. One of error, warn, info or debug. |
Privacy
| Variable | Default value | Description |
|---|---|---|
N8N_ | true | Set to false to stop n8n sending anonymous usage data. |
name: n8n-oidc
services:
n8n-oidc-init:
image: alpine:3.20
container_name: n8n-oidc-init
restart: "no"
network_mode: bridge
command:
- sh
- -c
- >-
mkdir -p /n8n &&
wget -q -O /n8n/hooks.js https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@8667d4dab6806586798c4f96919bac77d6352e69/Apps/n8n-oidc/hooks.js &&
echo "51243d919f9d0289f5312d1d2fe507b6f771e84afaa48ea105b868cad6d99757 /n8n/hooks.js" | sha256sum -c - &&
chown 1000:1000 /n8n /n8n/hooks.js &&
chmod 644 /n8n/hooks.js
volumes:
- type: bind
source: /DATA/AppData/$AppID/n8n
target: /n8n
bind:
create_host_path: true
deploy:
resources:
limits:
cpus: "0.50"
memory: 64M
reservations:
cpus: "0.00"
memory: 16M
labels:
icon: https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/icon.png
x-casaos:
id: com.icestore.n8n-oidc
volumes:
- container: /n8n
description:
en_US: Same folder as n8n's data. Holds the checked OIDC hook file.
n8n-oidc:
image: n8nio/n8n:2.30.1
container_name: n8n-oidc
restart: unless-stopped
stop_grace_period: 40s
network_mode: bridge
depends_on:
n8n-oidc-init:
condition: service_completed_successfully
environment:
- TZ=$TZ
- N8N_SECURE_COOKIE=false
- EXTERNAL_HOOK_FILES=/home/node/.n8n/hooks.js
- EXTERNAL_FRONTEND_HOOKS_URLS=/assets/oidc-frontend-hook.js
- N8N_ADDITIONAL_NON_UI_ROUTES=auth
- OIDC_ISSUER_URL=CHANGEME_OIDC_ISSUER_URL
- OIDC_CLIENT_ID=CHANGEME_OIDC_CLIENT_ID
- OIDC_CLIENT_SECRET=change-me
- OIDC_REDIRECT_URI=CHANGEME_OIDC_REDIRECT_URI
ports:
- target: 5678
published: "6111"
protocol: tcp
volumes:
- type: bind
source: /DATA/AppData/$AppID/n8n
target: /home/node/.n8n
bind:
create_host_path: true
deploy:
resources:
limits:
cpus: "2.00"
memory: 2048M
reservations:
cpus: "0.00"
memory: 512M
labels:
icon: https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/icon.png
x-casaos:
id: com.icestore.n8n-oidc
envs:
- container: TZ
description:
en_US: Your time zone. ZimaOS fills this in for you.
- container: N8N_SECURE_COOKIE
description:
en_US: Keep false when you open n8n with http://. Set it to true only when n8n is behind HTTPS.
- container: EXTERNAL_HOOK_FILES
description:
en_US: Path to the OIDC hook file. Do not change.
- container: EXTERNAL_FRONTEND_HOOKS_URLS
description:
en_US: Loads the SSO button on the sign-in page. Do not change.
- container: N8N_ADDITIONAL_NON_UI_ROUTES
description:
en_US: Lets the /auth/oidc routes work. Do not change.
- container: OIDC_ISSUER_URL
description:
en_US: The address of your login provider, like https://auth.example.com. It must serve /.well-known/openid-configuration.
- container: OIDC_CLIENT_ID
description:
en_US: The Client ID your login provider gave you for n8n.
- container: OIDC_CLIENT_SECRET
description:
en_US: The Client Secret your login provider gave you for n8n.
- container: OIDC_REDIRECT_URI
description:
en_US: Your n8n address plus /auth/oidc/callback, like http://192.168.1.10:6111/auth/oidc/callback. It must match the redirect URI set in your login provider.
ports:
- container: "5678"
description:
en_US: n8n web UI and webhooks, published on host as 6111.
volumes:
- container: /home/node/.n8n
description:
en_US: n8n database, encryption settings and the OIDC hook file.
x-casaos:
id: com.icestore.n8n-oidc
architectures:
- amd64
- arm64
main: n8n-oidc
author: HSinghHira
category: Productivity
developer: n8n GmbH (OIDC hook by Cameron Eagans)
icon: https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/icon.png
thumbnail: https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/screenshot-1.jpg
screenshot_link:
- https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/screenshot-1.jpg
- https://cdn.jsdelivr.net/gh/HSinghHira/IceStore@main/Apps/n8n-oidc/screenshot-2.jpg
title:
en_US: n8n (OIDC)
tagline:
en_US: n8n workflow automation with single sign-on through any OIDC provider.
description:
en_US: >-
Visit: [https://icestore.hsinghhira.me/app/n8n-oidc/](https://icestore.hsinghhira.me/app/n8n-oidc/) for full details
n8n with a bolt-on OIDC login, so you can sign in through Pocket ID,
Authentik, Keycloak or any other OIDC provider. It uses the community
[n8n-oidc](https://github.com/cweagans/n8n-oidc) hook. It is not an
official n8n feature.
**Features**
- "Sign in with SSO" button on the n8n sign-in page
- Accounts are created on first login
- The first person to sign in becomes the owner
- SQLite database and settings kept in the app data folder
- The hook file is downloaded and checked against a fixed SHA-256 hash
on every start
**How to use?**
1. Open n8n from the Zima OS dashboard.
2. Click **Sign in with SSO** and log in with your provider.
3. Build your first workflow.
tips:
before_install:
en_US: >-
Visit: [https://icestore.hsinghhira.me/app/n8n-oidc/](https://icestore.hsinghhira.me/app/n8n-oidc/) for full details
index: /
port_map: "6111"
scheme: http
is_uncontrolled: false
version: "2.30.1"
update_at: "2026-10-20"
release_notes:
en_US: |-
- Moved to IceStore. Port changed from 8469 to 6111.
- The hook file is now downloaded from the IceStore repo (same file, same hash).
- Removed N8N_PROTOCOL from the compose file; n8n already defaults to http. It is in the Variables tab.
- The OIDC hook was last tested upstream on n8n 2.1.1.
repo: "https://github.com/n8n-io/n8n"
support: "https://github.com/cweagans/n8n-oidc/issues"
docs: "https://github.com/cweagans/n8n-oidc#readme" ZimaOS
 CasaOS
 Homeio